Secure your entire stack with one AI-native AppSec platform

Security that
understands
the software
you ship.

Bring continuous pentesting, threat modeling, bug bounty triage, code security, dependency management, and AppSec compliance together. Every finding validated at runtime with authenticated test users, prioritized based on your application's context.

Casco product interface showing application discovery, authenticated security testing, proven findings, and retest progress.
Assets under protection
1B+
True positive rate
99%+
Better price-performance
vs. frontier models
5.8×

Trusted by
400+ companies

Archil
Blaxel
Microsoft
Crewai
Daytona
Gusto
Levelsfyi
Microsoft
Novig
Scout
Sixtyfour
Spreedly
Whop

Pick the capabilities you need. Or run them all together.

Every capability shares your application’s context and the same validation engine. Start with a pentest or bring findings from the tools you already use.

Continuous 24/7 Pentesting

Test the apps & APIs your users use.

Test authenticated workflows, APIs, and business logic, even behind Cloudflare challenges, CAPTCHAs, and firewall rules.

Explore continuous pentesting
Your Casco agent

Equipped with its own identity.

  • Email inboxSend & receive
  • Phone numberReceive SMS codes
  • TOTP deviceGenerate MFA codes

Signs in with

  • Username & password
  • MFA
  • Google SSO
  • Microsoft Entra ID
  • Magic Link
  • One-time SMS code
Authenticated testing
68%

of high/critical findings required signed-in access.
The highlighted portion represents findings requiring signed-in privileges; the rest required no privileges.
CrewAI

“In my 15 years working in cybersecurity, Casco is the first cybersecurity product that makes security testing high-quality, fast, and easy.”

Matthew BroomHead of Security, CrewAI
Watch full story
SDKs & Infrastructure Testing

Built to test developer tools.

Casco agents build test harnesses with your SDK, launch sandbox environments, and run code inside your infrastructure to test internal security boundaries and tenant isolation.

See Casco in action
Your Casco agent

Builds the harness. Runs the tests.

Build around your SDK

Your SDK
Agent-built harnessThe agent creates a harness to exercise your SDK and test its internal security boundaries.

Launch a sandbox

Tenant A
Run tests
Tenant B
Resources

Probe tenant isolation from within

Code & design

Catch risks before they ship.

Review designs, investigate source-code findings, and catch exposed secrets with your application’s context.

Explore code workflows
Connected workflows
Source code & CI
  • GitHub
  • GitLab (limited access)
  • Buildkite
Finding reporting
  • Jira
  • Linear
  • Asana (limited access)
  • Slack

* GitLab.com and Asana: limited access.

90%

more findings with source code connected.

Bars compare typical findings with and without source access. The comparison shows an observed association.
Scout

“In a matter of hours, Casco was able to find critical vulnerabilities that our other pentesters couldn't find for months.”

Bryan ChappellCEO, Scout
Watch full story
Cloud & configuration

Secure what runs your software.

Connect AWS, Google Cloud, Railway, and Vercel. Test assets, permissions, and configurations in the context of the software running on them.

Explore cloud security
Connected infrastructure
  • AWS
  • Google Cloud
  • Railway
  • Vercel
Services · Storage · Permissions
200%

more high/critical findings with cloud connected.

Bars compare typical high/critical findings with and without cloud access. The comparison shows an observed association in a small sample.
SixtyFour

“Casco is mission-critical for enterprise deals. We started the security assessment on a Friday and completed the procurement process by Monday.”

Saarth ShahCEO, SixtyFour
Watch full story
Dependencies

Know which updates matter.

Connect package advisories and exploit intelligence to your application’s context. Prioritize the vulnerable dependencies that matter.

Explore prioritization
Package advisories
  • npm
  • Rust crates
  • PyPI
  • Go
  • Maven
  • NuGet
  • RubyGems
  • Composer
87%

of audited codebases contained vulnerable open source dependencies.

Highlighted cells represent audited codebases containing vulnerable open source; the remaining cells represent the rest of the industry audit sample.

The security OS that understands your business

Casco connects your code, services, identities, and deployments so every investigation builds on what your application actually does.

Explore application context
Code, dependency, application, and cloud signals share one application context. Casco investigates, validates, and verifies fixes to deliver prioritized findings, verified fixes, and AppSec evidence while filtering out false positives and noise.
  • Code & design
  • Dependencies
  • Apps & APIs
  • Cloud

Application context

  • Code paths
  • Services
  • Identities
  • Tenants
  • Deployments

Casco validation engine

  1. Investigate
  2. Validate
  3. Verify the fix
  • Prioritized findings
  • Verified fixes
  • AppSec evidence
  • False positives & noise

Coverage that follows your stack.

Live workflows turn every signal into tested evidence, retained context, and a clear next action.

Connected operating layerHow Casco connects to your workflow.

Ask Casco questions from the tools you already use, connect live system context to each test, and route verified findings directly to the team responsible for the fix.

Customer agents

Stay connected to the pentest from the tools you already use.

Systems Casco tests

Connect source, cloud, CI, and runtime context to the test.

GitHubSource code
AWSCloud infrastructure
BuildkiteCI runtime
Google CloudCloud infrastructure
RailwayApplication runtime
VercelDeployment runtime

Team ticketing

Move validated findings directly into the team’s workflow.

SlackFinding notifications
LinearIssue creation

Every release starts with what Casco already learned.

Scope, identities, and proven attack paths carry forward. Casco tests what changed and replays the attacks that mattered.Explore continuous pentesting

  1. 01
    Retain contextScope and identities
  2. 02
    Test the deltaEvery approved release
  3. 03
    Replay proofVerified fix
Comparison of scanners, traditional pentests, and Casco continuous penetration testing
CapabilityScannerTraditional pentestCasco
TriggerScannerManually triggeredTraditional pentestScheduled engagementCascoEvery approved release
CoverageScannerKnown signaturesTraditional pentestManual samplingCascoAdaptive authenticated agents
ContextScannerStarts from scratchTraditional pentestEnds with the reportCascoScope and attack history retained
ProofScannerPotential weaknessTraditional pentestPoint-in-time narrativeCascoReproducible exploit evidence
Fix validationScannerRun another scanTraditional pentestBook a retestCascoReplay the proven attack

Keep security moving as fast as your software.

For engineering

Spend less time investigating alerts.

Get the application context, test evidence, and remediation guidance you need to move straight to the fix.

For security

Build a repeatable AppSec program.

Keep testing, triage, ownership, and retests in one workflow, so every finding shares the same context and has a path to resolution.

For procurement & compliance

Have the evidence ready when asked.

Share pentest reports, remediation status, and retest evidence to keep customer security reviews moving.

Compliance & procurement

Application security you can run continuously. Evidence for compliance audits and enterprise procurement.

Keep testing history, finding status, remediation records, and retest results together. Support SOC 2, ISO 27001, and HIPAA reviews with evidence from the work your team actually performs.

Casco pentest reports have cleared the toughest procurement processes at Microsoft, Google, AMD, and Apple.

United States flagFor government teams

Casco for Government

Continuous offensive security for government software. Test approved applications, infrastructure, and AI systems with security agents that prove exploitable paths and validate every fix.

Approved scope. Continuous proof.

  • Your boundaries, enforced.

    Define pre-approved targets and test scenarios, with scope controls enforced at the network level.

  • Coverage across your mission.

    Test authenticated apps, APIs, cloud infrastructure, networks, and AI workflows, including agents and MCP servers.

  • Evidence for every fix.

    Get reproducible exploit evidence and remediation guidance. Replay the original attack to confirm the fix.

Casco, explained

Frequently Asked Questions

Clear answers for security teams, engineering leaders, and anyone evaluating a modern pentest.

Ask about your scope
What is Casco?

Casco is an AI-powered penetration testing platform that helps security teams find, validate, and fix exploitable vulnerabilities. Its security agents test your applications and infrastructure, reproduce real attack paths, and provide evidence and remediation guidance. Casco also helps triage external security findings by investigating incoming reports and validating their impact in your environment, so your team can separate signal from noise and focus on the issues that matter. Explore security report triage

What is AI penetration testing?

AI penetration testing uses security agents to explore a running product, build a threat model, follow attack paths, and validate impact. Casco can add an offensive security engineer to guide the test and review findings when the scope calls for human supervision.

Which models does Casco use?

Casco uses a mix of commercial models and abliterated, open-source models. The model mix allows Casco to get more coverage and better cost-efficiency than individual models alone. Casco is part of the OpenAI Defense Collective, Anthropic Cyber Verification Program (Red Team Access), and other equivalent programs.

How does Casco know what to test?

Casco first discovers your applications, infrastructure, and networks. It maps domains, endpoints, authentication, roles, tenant boundaries, services, and AI interfaces. Casco learns from your application context, customer workflows, documentation, and public-facing artifacts. It uses that context to build scenario-based tests around potential issues in your system.

Does Casco prove that a finding is exploitable?

Yes. A finding includes the affected resource, reproduced impact, remediation guidance, and the code or request used to validate it. Human verification is available when your security or procurement process requires it.

What does Casco test?

Casco tests approved web applications, APIs, cloud infrastructure, mobile applications, browser extensions, AI applications and agents, MCP servers, and internal or external networks.

Is Casco safe to run against production?

Yes. Casco is safe to run against production. It operates only inside approved targets, accounts, time windows, and rules of engagement. It does not perform DDoS or resource-exhaustion attacks. Stable source IPs, per-request IDs, and network-level scope controls keep testing traceable and constrained. Read about Casco’s network-observability safeguards

Can Casco test black-box applications?

Yes. Casco only needs a single application entry point to begin black-box testing. If your application is self-serve, Casco security testing agents can automatically sign up and begin testing authenticated workflows.

Can Casco test grey-box applications?

Yes. Casco can use optional source code, cloud context, architecture details, documentation, and test credentials to make scenario-based testing more precise. Integrations are available for AWS, GCP, Railway, Buildkite, Jira, Linear, and GitHub.

How does Casco test authenticated applications? Are there any restrictions?

Casco supports authenticated testing through CAPTCHA, MFA, SSO, Microsoft Entra ID, magic links, and SMS one-time passwords. Its security testing agents have dedicated identities, including their own email inboxes, phone numbers, and TOTP devices. They can complete login flows and test the approved roles and tenant boundaries behind them. Explore enterprise authentication support

Can Casco test email workflows beyond authentication?

Yes. Casco agents have their own email inboxes and phone numbers, so they can exercise email workflows end to end. Within the approved scope, they can test email-abuse scenarios as well as login flows such as magic links and SMS one-time passwords. Explore application workflow testing

How is Casco different from a scanner or annual pentest?

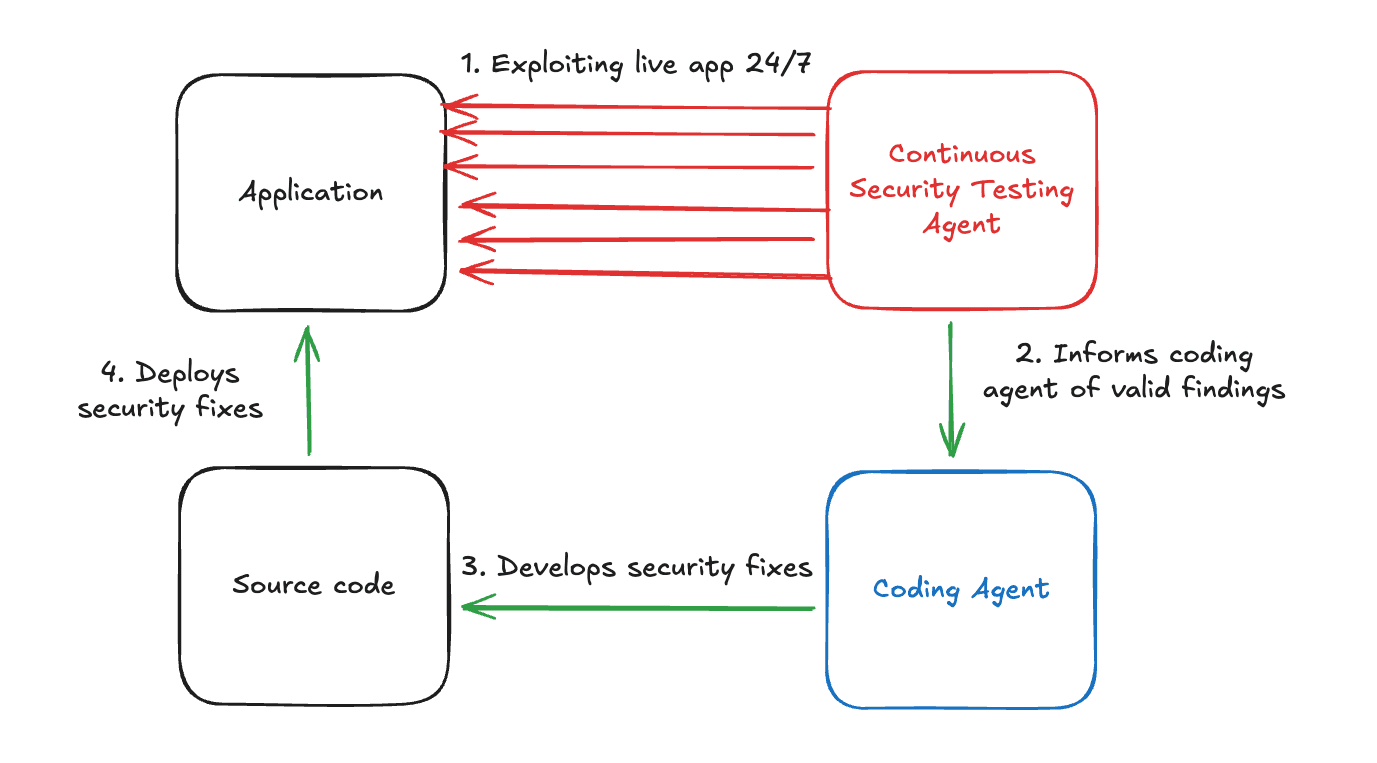
Scanners look for known patterns. Annual pentests capture one version of a product. Casco combines adaptive agents, retained application context, optional human review, and exact-attack retesting after releases and fixes. It can run 24/7. See how continuous pentesting works

Can I use Casco for SOC 2 and ISO 27001?

Casco Supervised provides human-reviewed findings and can provide an attestation letter to support your security review. Confirm the required test scope and documentation with your auditor before the engagement. Explore human-supervised pentesting

Can I use Casco for procurement?

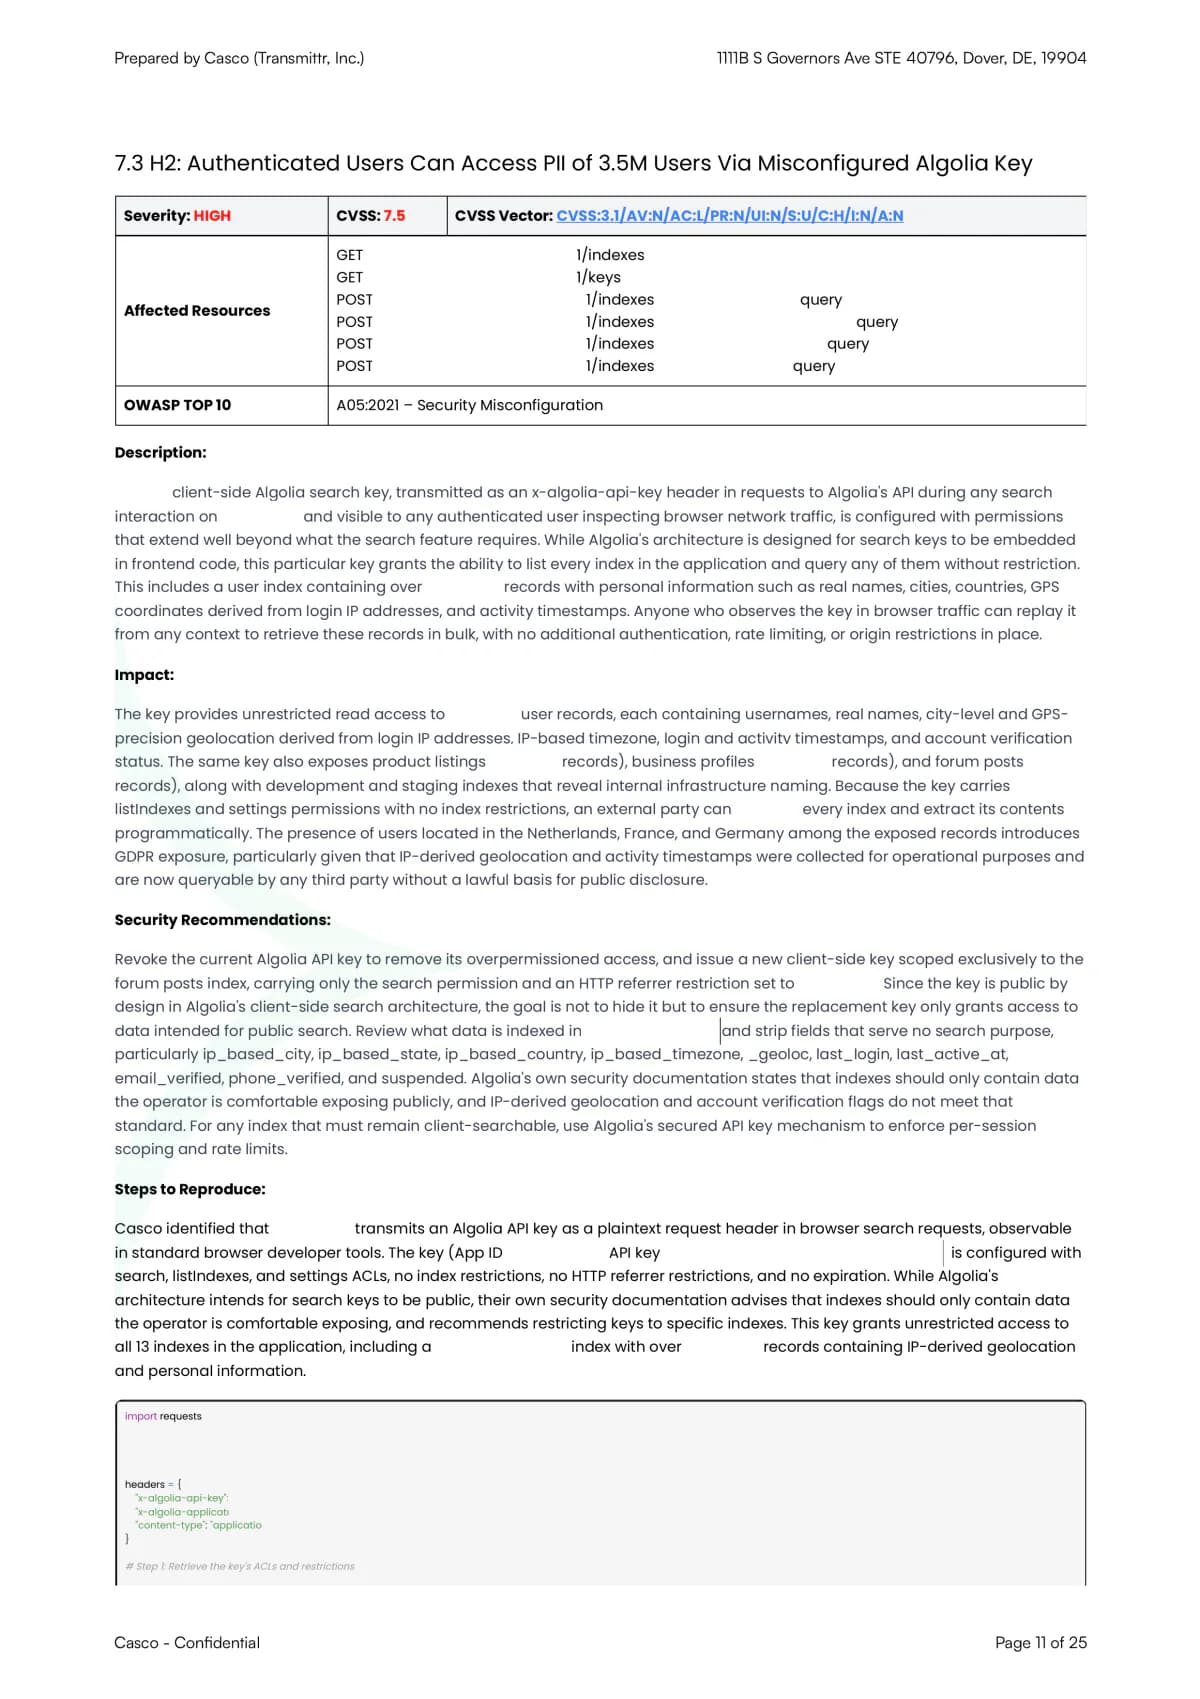
Yes. Casco pentest reports have cleared security and procurement reviews at Microsoft, Google, AMD, and other major enterprises. Each report packages approved scope, reproduced impact, evidence, remediation guidance, and retest results for buyer and security-team review. Optional human verification is available when required. Get a sample pentest report

How quickly does Casco deliver results?

Casco delivers findings immediately as they are validated. If you require a human-approved pentest, Casco delivers it within five business days.

How is Casco priced?

Casco’s pricing depends on scope and the frequency of product changes. Book a demo to learn more.

What happens after a vulnerability is fixed?

You can configure Casco to automatically replay the original attack. The retest records when the finding is remediated.