What We're Watching
Malware used to have the decency to hide.
Spyware hides behind nuclear and bioweapons text
Socket found worms aimed at bioinformatics and MCP developers that open with a comment block of fake system instructions and weapons-related text. JavaScript ignores the comment. An LLM triage tool may not, and can refuse or misclassify the file before anyone looks at the obfuscated payload underneath.
Shai-Hulud worm ships in a compromised Tensorlake release
On October 8, tensorlake@0.5.144, an npm package for AI agent sandboxes, shipped with a credential stealer. It writes editor and Claude Code configs so it runs again whenever the repo is opened. According to StepSecurity, revoking the stolen token triggers a wipe of your home directory.
An exploited Windows Shell zero-day bypasses Mark of the Web
October's Patch Tuesday fixed more than 1,400 flaws. One of them, CVE-2026-96951 (CVSS 8.8), is already being exploited: a crafted file bypasses Mark of the Web, so Windows doesn't flag it as downloaded.
Our Take
This worm wraps an ordinary payload in fake system instructions and weapons-related text, betting that a language model reading the file will refuse or misclassify it. It isn't a real bypass. YARA, entropy checks, and a human with a deobfuscator still catch it. It only works on a pipeline that asks the model first and checks nothing after.
That setup is more common than it should be. A lot of teams added an LLM to triage, code review, or an agent workflow this year without deciding what happens when the content it reads contains instructions. Three things to check: Is file content passed to the model as untrusted data? When the model refuses or times out, does the file go to a human instead of being marked clean? And do deterministic checks still run regardless of what the model says?
If you don't know the answers, test it. Feed your tooling a file like this one, see where it ends up, and fix whatever let it through.
Updates from Casco
A new guide on the blog and two upcoming events.
 Remediation guide
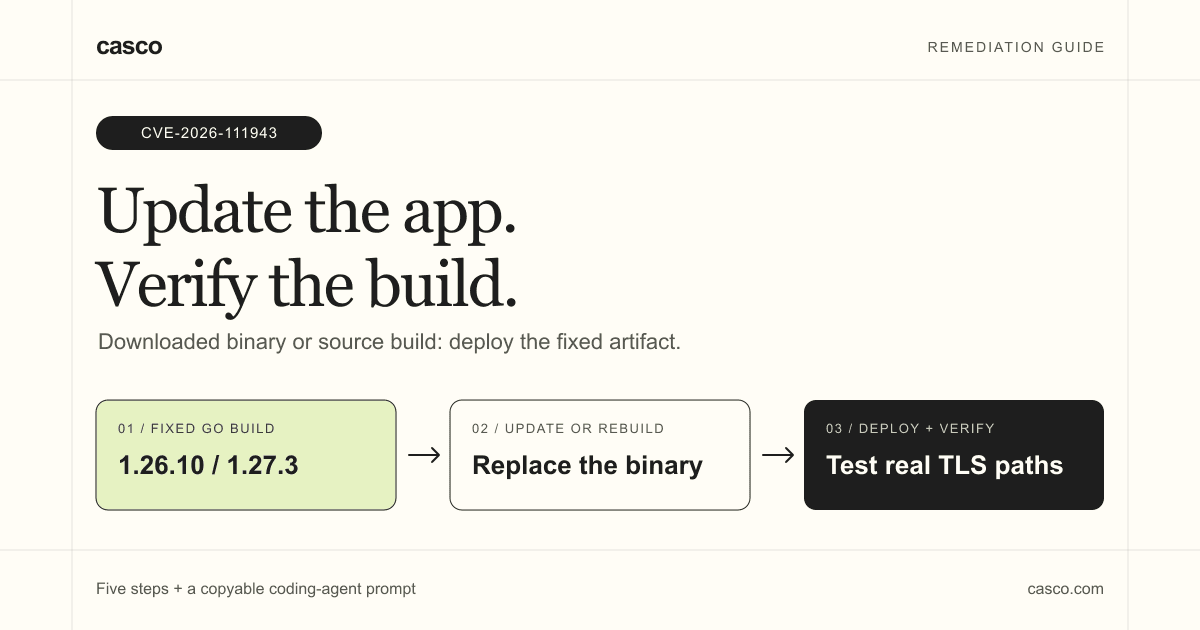
How to fix CVE-2026-111943 in Go apps and binaries.
Mozilla confirmed that eMudhra intermediate certificates were compromised, and Go shipped an urgent update (1.26.10 and 1.27.3) that stops trusting the affected keys. Go binaries also show up in places teams don't track, like CLIs, container images, and tools bundled inside Python or JavaScript packages, so you can be affected without writing any Go.
René wrote up how to find those binaries and confirm the patched versions are the ones actually running, not just downloaded. The post also includes a prompt you can give a coding agent to do the inventory.
Check out the full post
Happy hour in Minneapolis. If you're in town for BSides Twin Cities, join us this Friday, October 23, from 6 to 8 PM at Day Block Brewery (1105 Washington Ave S). Pints and slices are on us. Registration needs host approval.
Request to join
Archil's first hackathon, at our office. Archil is hosting Agents Need Solid Ground at Casco's SoMa office on Tuesday, November 10, from 6 to 10 PM PT, with $50K in prizes. It celebrates Archil's new $10/month plan for individual developers.
RSVP for the hackathon
A practical next step
Can a single file steer your AI tooling?
Casco tests whether your models, agents, and copilots can be manipulated by the inputs they're meant to analyze.
Casconaut Highlight
One small recommendation from the people behind Casco.
This issue's Casconaut
Eleanor Sigel
Security Architect
Currently recommending
Protomartyr
I recommend Protomartyr, a post-punk band from Detroit. The singer sounds like he has read every incident report ever filed and was not surprised by any of them.
Start with The Agent Intellect. It holds up on a long run and on a long day of reading patch notes.